Delegation framework15 Oct 2026NEW
The AI-enabled vCISO
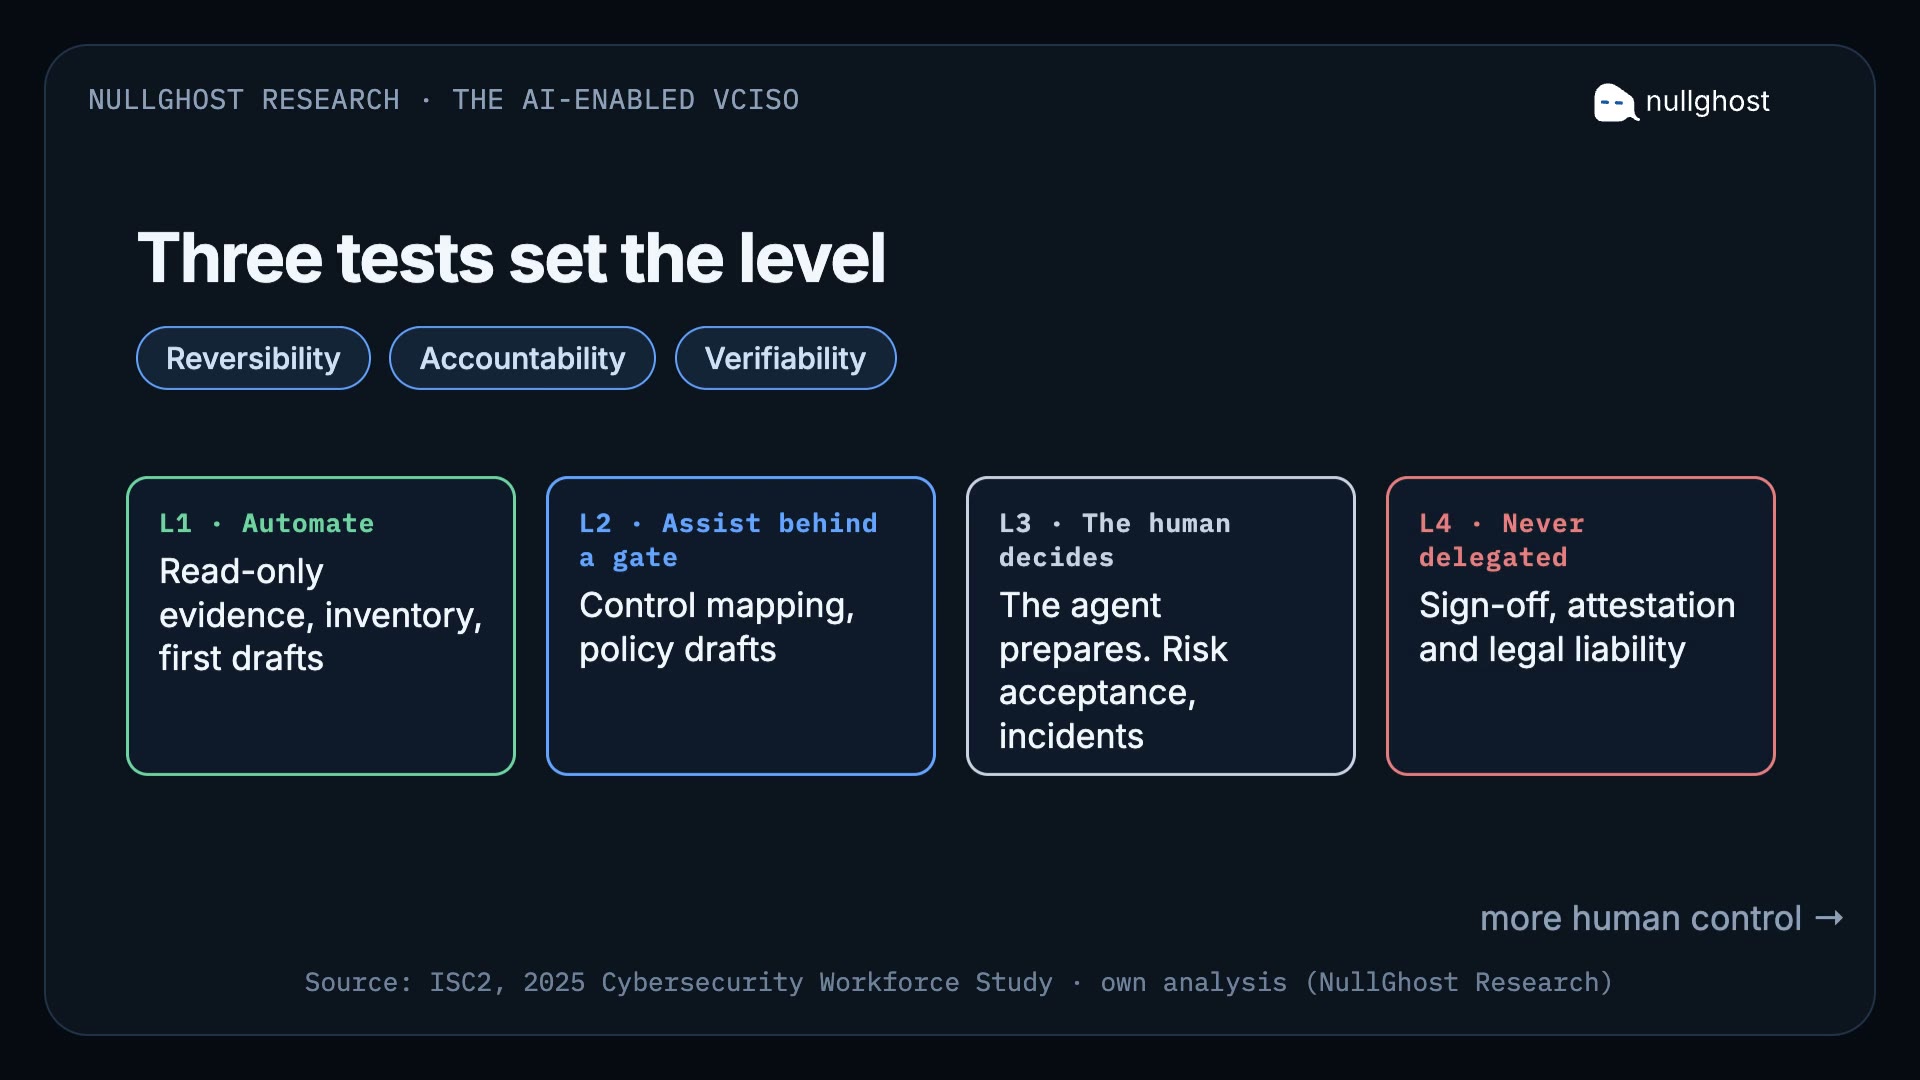
What gets delegated to an agent, what gets verified and what cannot be delegated. A four-level ladder and a measurement protocol, with explicit sources and limits.
How a small team links the governance of its AI use to the traceability of an agent operating tools in a lab.
A pentest with AI is not evaluating the security of the AI; a VM is not isolation; traceability is not conformance.
The paper describes the observed architecture of a lab where an agent drives tools over MCP inside a Kali VM against authorized own targets, and reads it against the public scope of ISO/IEC 42001:2023 and ISO/IEC 27090:2026. It proposes a governance-to-evidence table with the real status of each activity, mostly pending.
It reuses NullGhost’s evidence protocol: authorization, test plan, negative results as “not observed under these conditions,” independent verification and integrity via hashes. It is a single operation over own targets, not a benchmark; it records silent failure, browser differences and automation errors as limitations. Neither standard was read in full.
What gets delegated to an agent, what gets verified and what cannot be delegated. A four-level ladder and a measurement protocol, with explicit sources and limits.
What has been measured, what has been projected and what has been legislated. Each source is tagged by verification level and no date is promised.
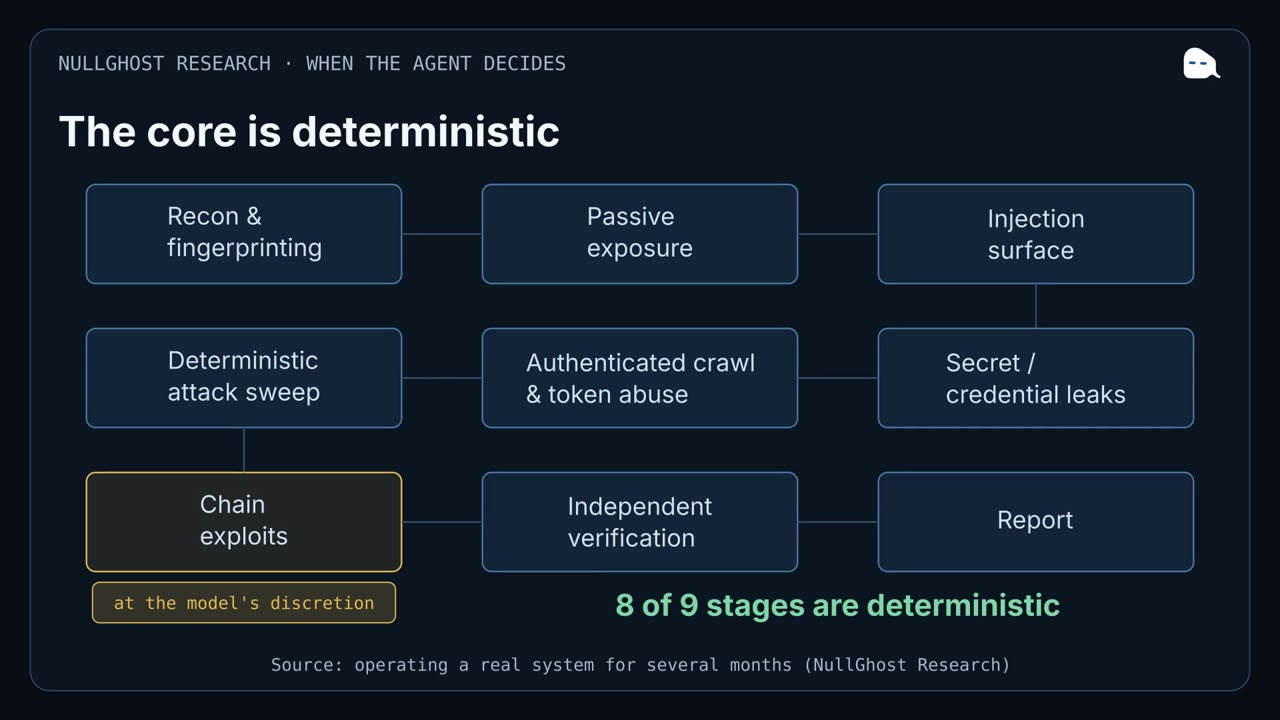
Ten lessons on coverage, verification and silent failures from operating an offensive security agent.