Evidence reviewOct 12, 2026
From today's AI to superintelligence
What has been measured, what has been projected and what has been legislated. Each source is tagged by verification level and no date is promised.
Field observations and industry analysis, with video, charts and a PDF paper. Every figure with its source and its limits.
What gets delegated to an agent, what gets verified and what cannot be delegated. A four-level ladder and a measurement protocol, with explicit sources and limits.
What has been measured, what has been projected and what has been legislated. Each source is tagged by verification level and no date is promised.
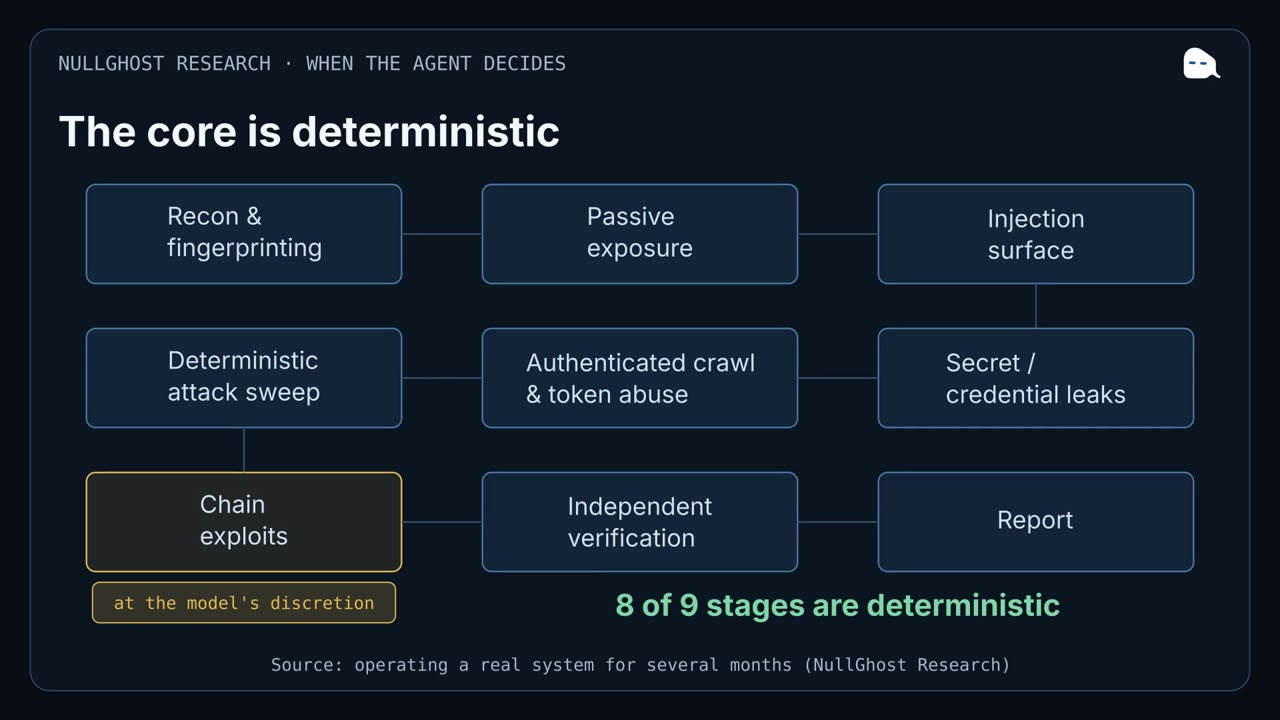
Ten lessons on coverage, verification and silent failures from operating an offensive security agent.
Identity, authorization and delegation: questions to ask before putting AI agents into operation.
A verification layer between an agent’s decision and its action. We examine the pattern through TypeSafe AI / Jev.
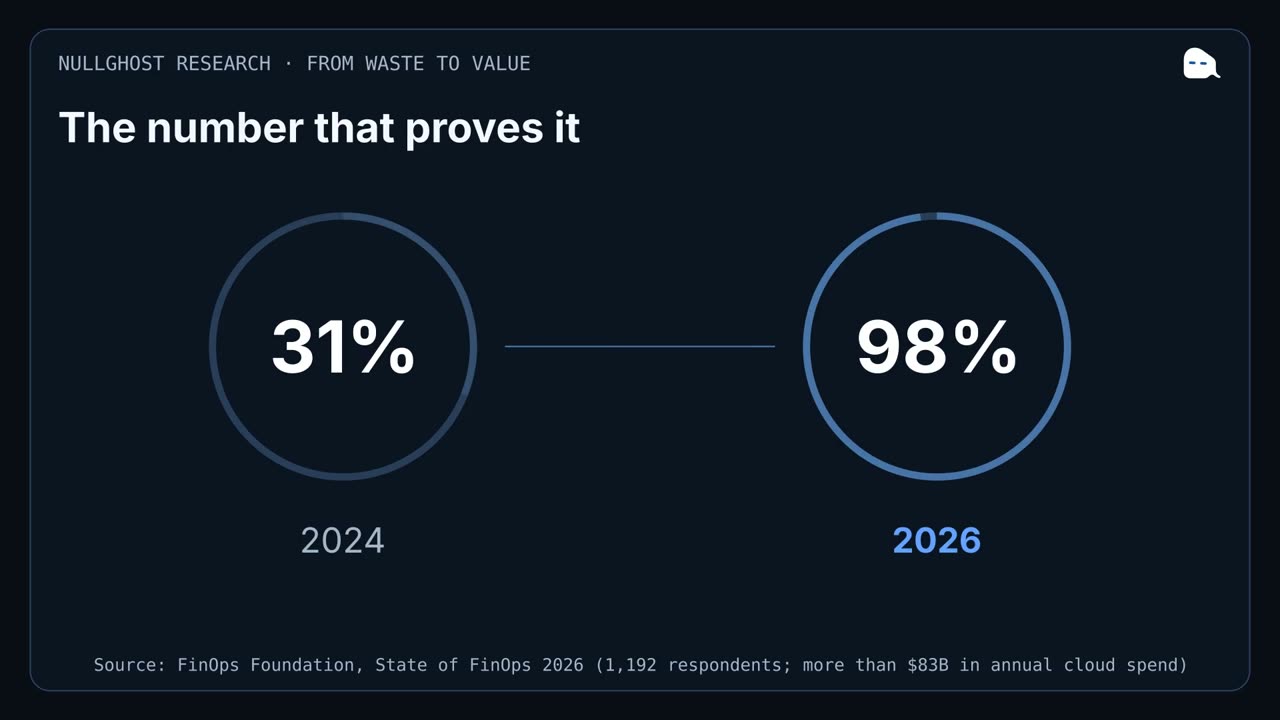
What changes when AI spend enters the FinOps conversation. A reading of State of FinOps 2026.
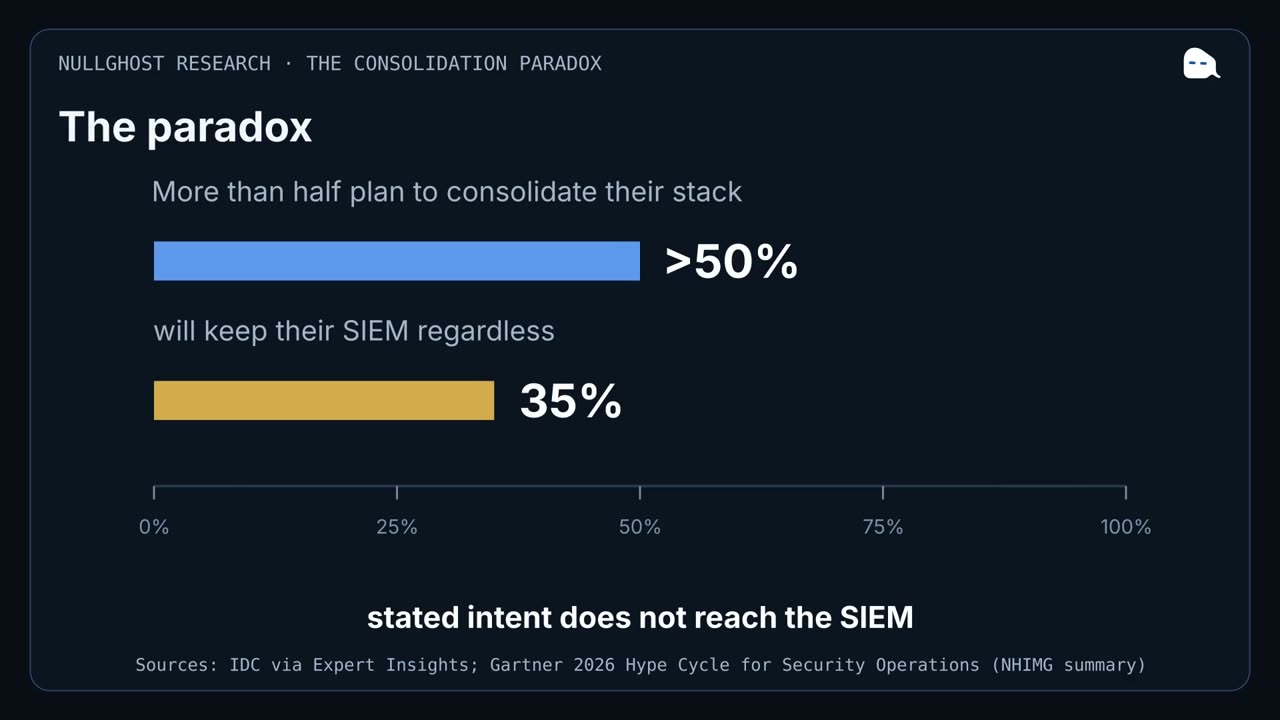
More than half say they're consolidating their security stack. 35% will keep their current SIEM regardless. A reading of the 2026 SIEM market.
Every chart uses only figures published in the summary or the paper, with its source and its limits.
Selected references to understand risk. Applicability depends on your technology, version and configuration.
Command injection affecting Linksys RE6250, RE6300, RE6350, RE6500, RE7000 and RE9000. Check the record’s affected products and versions before determining exposure.
Official CVE record ↗A reference for reviewing prevention, preparedness and response. Use it to guide a control review with your team.
CISA — #StopRansomware Guide ↗Explore what Kirux can do and define with us what applies to your environment.